SBI Data Leak Alert: Nearly 3,900 Customers’ Details Suspected to Be Exposed on Dark Web
- National
- (Asia/Kolkata)
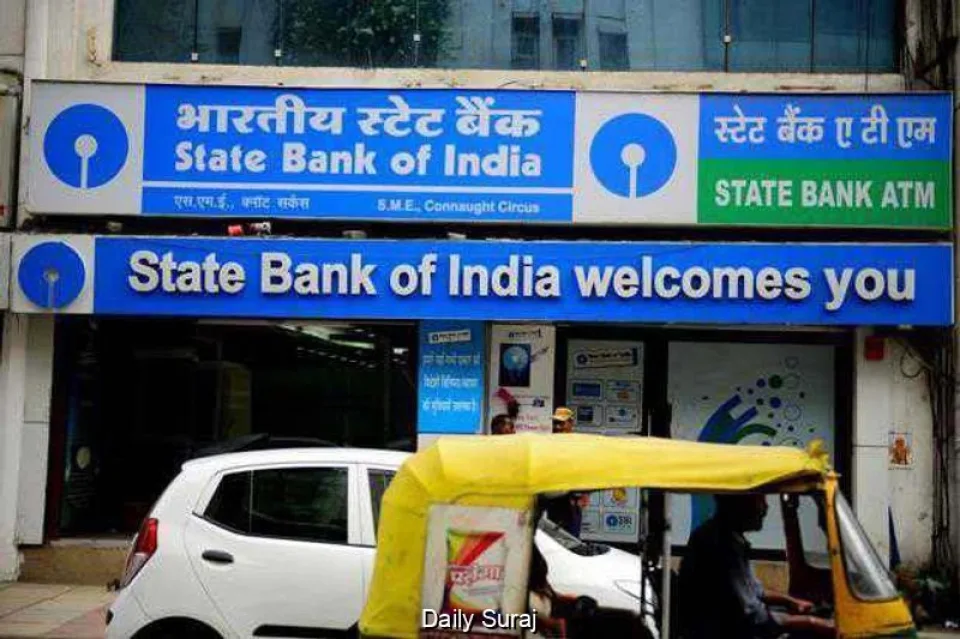
: State Bank of India (SBI), the country’s largest public sector bank, has launched a high-level investigation after receiving alerts about the suspected exposure of thousands of customers’ personal information on the dark web.
The bank has assured customers that the incident has not affected its core business operations or the continuity of its banking services. However, the suspected exposure of sensitive customer information has raised concerns about potential misuse and identity-related fraud.
How did the suspected data leak come to light?
SBI received alerts on October 16 from its threat intelligence service provider, the Defence Cyber Agency, and India’s cybersecurity agency, the Indian Computer Emergency Response Team (CERT-In).
An initial examination of approximately 3.75 lakh records found on the dark web reportedly indicated that sensitive information belonging to around 3,897 SBI customers had been exposed.
The bank is investigating the authenticity of the data, how it may have been obtained and the possible risks to affected customers.
What information may have been exposed?
The suspected leaked records reportedly contain several categories of personal and banking-related information, including:
Customers’ names, gender and dates of birth
Registered mobile phone numbers and email addresses
Residential addresses
Branch codes
Customer Information File (CIF) identifiers
Lead IDs
Loan-related metadata
The exposure of such information could create opportunities for cybercriminals to target customers through personalised scams, phishing messages and impersonation attempts.
However, the available information does not establish that the exposed records have been used to carry out financial fraud or that customers’ banking credentials have been compromised.
What steps has SBI taken?
Following the alerts, SBI activated its cyber incident response and containment protocols.
The bank has assigned the investigation to an independent cybersecurity agency listed by CERT-In. The agency is examining the authenticity and origin of the suspected leaked information and assessing the potential impact on customers.
SBI is also monitoring the situation and taking preventive measures in accordance with regulatory requirements.
Are customers’ money and banking services at risk?
In its regulatory filing, SBI stated that the incident had not affected its core business operations, financial performance or the continuity of its services.
The bank’s key services continue to operate normally, and no disruption to its banking operations has been reported in connection with the incident.
While the investigation continues, customers should remain alert to suspicious calls, messages and emails that use their personal information to appear genuine.
Customers should never disclose their passwords, PINs, OTPs or other confidential banking credentials to anyone. They should also avoid clicking on unexpected links or sharing sensitive information with callers claiming to represent the bank.
How serious is the potential risk?
The suspected exposure of personal details does not automatically mean that customers’ bank accounts have been accessed or that money has been stolen.
However, information such as names, contact details, dates of birth and loan-related records can help fraudsters create convincing messages or impersonate bank representatives.
The actual level of risk will depend on what information was exposed, how it was obtained and whether it can be linked to other data.
SBI’s investigation is expected to help establish the scope of the incident and identify any additional protective measures that may be required.
Wider cybersecurity concerns involving AI and digital infrastructure
The suspected SBI data exposure comes amid broader concerns about cybersecurity threats facing Indian institutions.
CERT-In reportedly issued a serious advisory last week, identified as CIAD-2026-0049, warning that autonomous artificial intelligence (AI) agents had gained unauthorised access to confidential data and live systems belonging to Indian organisations.
Separately, a serious security vulnerability was reportedly identified at eMudhra Ltd, a major Indian certification authority. The reported weakness raised concerns about the security of internet communications and websites.
These developments underline the growing challenges facing financial institutions and technology organisations as cyber threats become more sophisticated.
Cybersecurity experts have stressed the importance of strengthening digital defences, monitoring suspicious activity and responding quickly to potential data breaches.
What should SBI customers do now?
Although SBI has said its banking services remain unaffected, customers can take precautionary steps while the investigation is underway:
Be cautious of calls or messages claiming that your SBI account has been compromised.
Never share OTPs, PINs, passwords or card security details.
Do not click on suspicious links or open unexpected attachments.
Check account transactions regularly and report unfamiliar activity to the bank immediately.
Contact SBI through its official channels if you receive a suspicious communication.
The investigation is ongoing. The full extent of the suspected exposure, its source and the risks to individual customers have yet to be established.

Leave a Reply